A cybersecurity risk assessment is a structured review of where your business is exposed, what an attack would cost you, and which fixes deserve budget first. For small and midsize businesses, it’s also the document auditors, insurers, and prime contractors ask for by name. Done properly, it turns “we should probably do something about our security” into a prioritized list you can act on.
Unfortunately, many small businesses skip risk assessments. The UK government’s 2025/2026 Cyber Security Breaches Survey found that only 41% had completed a cybersecurity risk assessment in the last 12 months, down from 48% the year before. Meanwhile, the Hiscox Group found that 59% of small and midsize businesses were attacked in the past year. And a third of those companies were fined on top of the attack itself.
The fact of the matter is, a well-executed cybersecurity risk assessment is one of the best ways to strengthen your business’s defenses and reduce long-term risk.
In this article, we’ll break down what a cybersecurity risk assessment is and why it’s a smart, strategic investment for any SMB.
Table of Contents
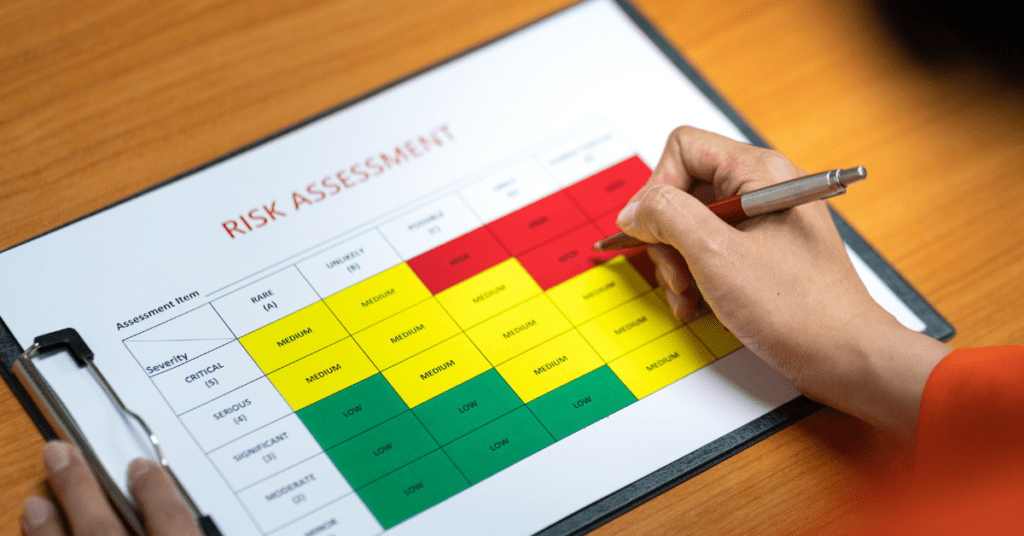
What Is a Cybersecurity Risk Assessment?
As the term implies, a cybersecurity risk assessment assesses cyber risks across an organization. It identifies the data and devices within the organization and determines whether they are protected against cybercriminals.
The assessment outcome is then used to enhance the organization’s security posture so that it can better face current and future threats.

The Cost of Inaction: Why Risk Assessments Are Essential
While these assessments aren’t new, many SMBs have historically overlooked them. But that mindset is outdated.
Because even the smallest businesses – with just a few employees – now rely on information technology and information systems to do business.
Even today, it’s still possible to find small business owners who believe that cybercriminals only target large enterprises with massive quantities of data on their servers and equally large piles of money in their bank accounts.
Unfortunately, this hasn’t been the case for quite some time.
The Data Says it All...
In 2015, Symantec, a provider of industry-leading antivirus and security software, revealed that some 43% of cyberattacks were directed at organizations with 250 employees or less. Cybercriminals became increasingly interested in SMBs because they saw them as easy prey…and many still are.
Fast forward to today, basic cybersecurity adoption remains alarmingly low among smaller organizations. Even as threats grow more advanced.
Many businesses haven’t implemented fundamentals like:
- MFA / Passkeys
- Role-based access controls
- Even strong passwords

Strong passwords are the foundation of your business’s cybersecurity strategy. Without them, your organization could be vulnerable to costly breaches and cyberattacks. Add these best practices to your password policy.
Recovery costs continue to soar (like ransomware, which now averages $2.73 million). So, there’s never been a more important time to assess your cybersecurity risks and take action before threats become losses.

Why Cybersecurity Risk Assessments Are Worth the Money
It’s easy to dismiss cybersecurity risk assessments as yet another technology-related expense.
Yes, it is…AND it is an investment in your organization’s future. Here are just four of many examples.
1. Reducing the Risk of a Cyberattack
The most crucial benefit of cybersecurity risk assessments is that they help reduce the risk of a successful cyberattack by identifying risks and proactively improving security defenses.
In recent years, cybercriminals have shifted focus toward smaller businesses with smaller cybersecurity budgets. That’s because these businesses are typically easier to breach and very likely to pay a ransom (which we do not recommend).
The COVID-19 pandemic made SMBs even more attractive targets because it forced employees to work remotely, often using poorly secured personal devices.
2. Lowering Long-term Costs
Even a relatively minor cybersecurity incident can create a vast financial disruption for SMBs. Ponemon Institute estimates that downtime can cost small businesses between $8,000 and $74,000 per hour. However, the associated reputation damage and loss of trust may hurt your business much more in the long run.
A cybersecurity risk assessment identifies risks before cybercriminals can exploit them for their own gain. That makes it one of the best investments any SMB can make.

Learn the financial impact of cyber threats on your business’s data. Plus, unlock the financial implications of in-house vs. outsourced cybersecurity.
3. Helping Achieve Compliance
Some SMBs are legally required to run regular cybersecurity risk assessments under regulations like:
- PCI DSS (Payment Card Industry Data Security Standard)
- HIPAA (Health Insurance Portability and Accountability Act)
- CMMC (Cybersecurity Maturity Model Certification)
Safeguard patient information and foster a strong reputation as a trusted healthcare provider with this self-assessment.
What’s more, cyber insurance carriers want to see the same thing. Before they’ll quote you, they’ll ask a long list of questions about your security controls, and if you’ve already done an assessment, it’s much easier to achieve the desired outcome.
Empower your company with CMMC knowledge. This guide covers the process, benefits, maturity levels, and how to prepare for your CMMC audit.
4. Generating Self-awareness
Cybersecurity risk assessments deliver clarity on where your defenses fall short.
- 1. They give decision-makers helpful information about people, processes, and technologies. This knowledge can then be used to make informed decisions about the organization’s future.
- 2. They also enhance cross-department communication and promote visibility because they require input from multiple stakeholders.
Simply put, these assessments help you invest in improvements that deliver real ROI by:
- Reducing risk
- Avoiding costly breaches
- Strengthening your business’s resilience

Who Should Perform a Cyber Risk Assessment?
The Challenge
In large organizations, cybersecurity risk assessments are typically performed by in-house personnel familiar with the organization’s network infrastructure, data flows, and information systems.
The problem is that many SMBs don’t employ any IT staff and are, therefore, unable to thoroughly assess how protected important data and devices are against cybercriminals.
The Solution
SMBs can easily outsource cybersecurity risk assessments to a third party – even if you have IT staff.
Teal brings deep experience conducting cybersecurity risk assessments for businesses and nonprofits in Minneapolis, Orlando, and Washington, DC. We’ve helped organizations in these regions protect sensitive data, close security gaps, and reduce the impact of cybercrime.



If you’ve never had a cybersecurity risk assessment – or it’s been years since your last one – now is the time.
Contact one of our senior advisors to learn more about our cyber risk assessment services and start your journey to a more financially secure future.